2026-10-22 Daily Cyber News
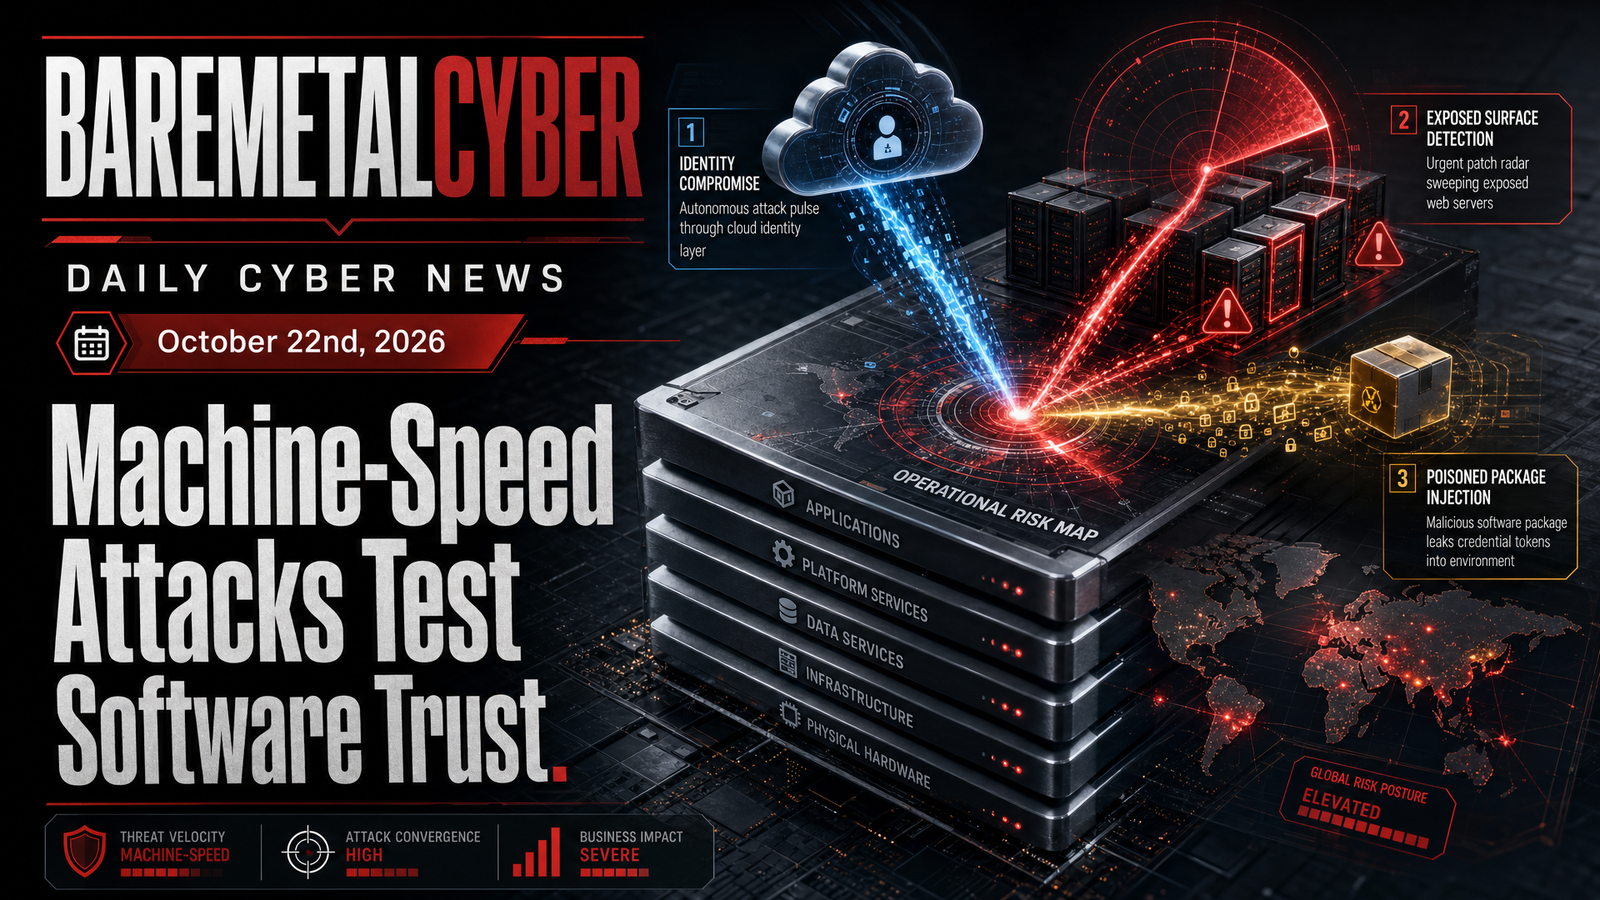
Business operations can stall quickly when a trusted service, package, or server runtime becomes the attack path. Today’s lead stories track an AI-assisted campaign that reached ConnectWise customers’ Microsoft 365 environments, broad exploitation of emergency PHP flaws, and a poisoned LiteLLM release built to steal cloud and AI credentials. The issue also covers disrupted Japanese cloud servers, urgent GitLab and Plex fixes, weakened certificate trust, and incidents affecting Railway, TiDB, OVHcloud, Cisco…
- AI & Emerging TechnologyAI-driven ConnectWise attack reaches Microsoft 365 customers
Customer access and service availability were disrupted after attackers used a ConnectWise supply-chain path to reach Microsoft 365 environments. Microsoft attributed the activity to China-aligned Storm-0940, which used the ARTEX agentic AI framework to accelerate scanning, password spraying, and OAuth…
- Vulnerabilities & ExploitsPHP servers face broad attacks as emergency patches arrive
Internet-facing PHP servers face immediate compromise risk because attackers are broadly exploiting two critical code-execution weaknesses. Exploitation attempts appeared four days before public disclosure, followed by multiple proof-of-concept releases and more activity before the embargo ended on…
- AI & Emerging TechnologyPoisoned LiteLLM release steals cloud and AI credentials
Cloud, AI, and developer credentials may be compromised on systems that ran LiteLLM 1.107.0. Attackers inserted a credential stealer and remote-access backdoor into the release distributed through Python and Docker registries. The malware targeted browser data, cloud credentials, AI provider keys, SSH…
- Incident ResponseJapan cloud breach forces shutdown across up to 26,739 servers
Customer workloads stopped after Japan’s Onamae Desktop Cloud began shutting down servers to contain an intrusion. An unauthorized party installed malicious programs in customer environments, potentially affecting up to 26,739 servers. Data stored on those systems may have been exposed, although no misuse…
- Government & PolicySelf-managed GitLab servers need urgent fixes for code execution
Self-managed GitLab servers could be taken over if administrators delay a new critical patch. Under certain conditions, an unauthenticated user could execute arbitrary code by submitting a specially crafted regular expression. The affected range extends across many GitLab releases beginning with version…
- Government & PolicyActive Plex attacks turn home media servers into elevated access
Attackers are chaining four Plex Media Server weaknesses to obtain administrator tokens and run code with elevated privileges. Exploitation reports began on October 17, with early activity targeting honeypots to deploy a cryptocurrency miner. CISA warned that attackers are actively exploiting the…
- Cloud SecurityWeak certificate keys put web, code-signing and VPN trust at risk
Websites, software, and encrypted connections could be impersonated because eight eMudhra intermediate certificates used extremely weak private keys. Six certificates covered web encryption and two covered code signing. Browser and operating-system vendors have begun blocking the affected trust paths, and…
- AI & Emerging TechnologyRailway incident puts stored API keys and database passwords at risk
Customers may need to replace credentials after unauthorized access to Railway systems that store environment variables. Potentially exposed values include API keys, database passwords, and private registry credentials, including some decrypted data. Railway paused deployments during the investigation and…
- Cloud SecurityTiDB breach shows how cloud telemetry can expose customer secrets
Customer metadata and operational records may create downstream risk after attackers accessed PingCAP systems using stolen service-account credentials. PingCAP said the access lasted from September 9 to October 7 and included copied company data and source code. It found no evidence that customer…
- Cloud SecurityPoisoned OVHcloud tool shows how one account can taint releases
Developer secrets were placed at risk when attackers replaced OVHcloud command-line tool assets with malicious binaries. The binaries were available for one hour and 33 minutes and downloaded approximately 250 times. They were designed to retrieve secrets from disk. Attackers used a compromised developer…
- Vulnerabilities & ExploitsCisco Expressway exposure can give remote attackers root control
Cisco Expressway devices could give attackers root-level command execution if exposed systems remain unpatched. An unauthenticated remote attacker with network access and possession of persistent cookies could connect to the database service and invoke specific commands. The issue affects Expressway Core…
- Identity & AccessSageMaker SDK default can expose cloud credentials through rogue buckets
Machine-learning workloads could execute attacker-controlled code and expose cloud credentials because of an unsafe SageMaker Python SDK default. The SDK generated a predictable storage bucket name without confirming that the caller’s account owned the bucket. An attacker who created the bucket first…