2026-11-20 Daily Cyber News
Essential services can stall when attackers reach the systems that manage people, infrastructure and trusted software. Today’s issue examines a cyberattack that disrupted European Commission personnel services, an actively exploited path to administrative control of VMware environments, and malicious releases of Microsoft’s official AI agent package that stole developer credentials. It also covers urgent NGINX updates, early Java attack activity and exploitation of internet-facing Cisco collaboration gateways.…
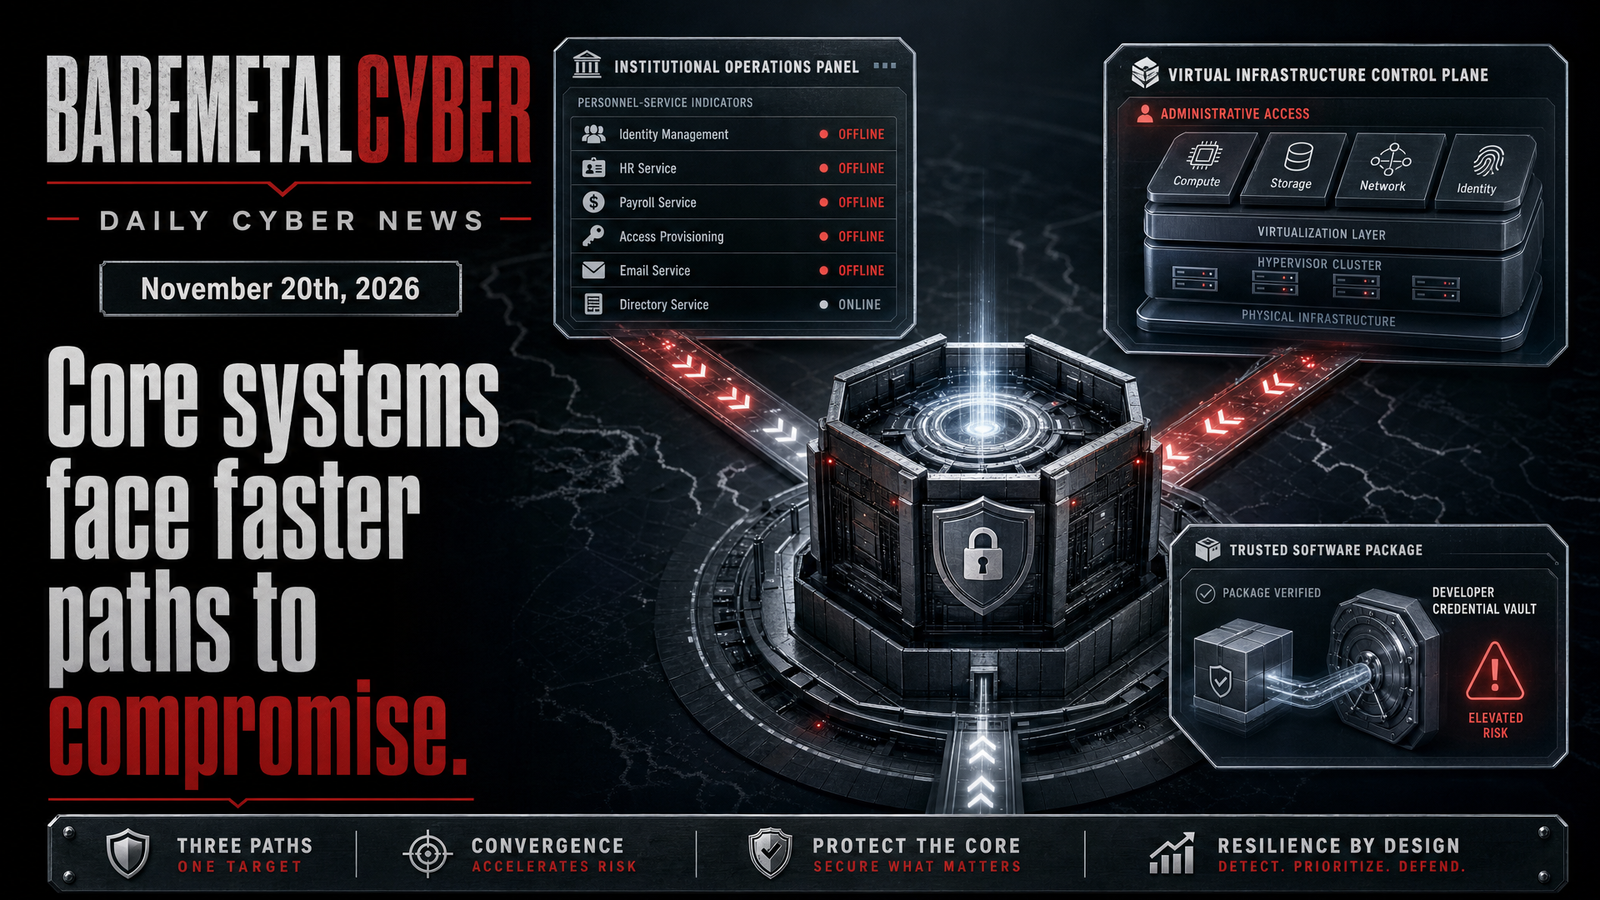
- Threat IntelligenceEuropean Commission attack disrupts critical personnel services
European Commission personnel services were disrupted for more than 10 days after a cyberattack detected on October 22. Affected functions reportedly included payroll, leave requests, medical reimbursements and translation services. The Commission took several services offline as a protective measure and…
- Vulnerabilities & ExploitsVMware control servers targeted through an authentication bypass
Attackers gained administrative access to VMware vCenter servers through an authentication bypass that has now been patched. Forensic evidence indicates a suspected China-linked group used the weakness in early September after first compromising BeyondTrust Remote Support and moving through internal Linux…
- Cloud SecurityMalicious Microsoft AI package steals developer credentials
Two releases of Microsoft’s official agent-framework package on the Python Package Index contained credential-stealing code. Versions 1.26.1 and 1.26.2 executed a startup hook when Python launched, even if developers never imported the framework. The code collected secrets, cloud and developer…
- Vulnerabilities & ExploitsNGINX servers need urgent updates as public demonstrations spread
Five serious NGINX weaknesses can let unauthenticated attackers crash workers or potentially run commands under specific configurations. The most concerning issue affects servers with HTTP/2 enabled and has existed since NGINX 1.9.5. Public demonstrations are available, although no exploitation in the…
- Vulnerabilities & ExploitsJava attack attempts begin while product fixes remain uneven
Attackers have started probing for a Java runtime weakness that can affect several enterprise applications. More than 150 matching requests from five IP addresses had been observed by early November 19, but those sensors had not confirmed successful intrusions. Exposure requires an affected Java release…
- Vulnerabilities & ExploitsCisco collaboration gateways exploited after public code appears
Attackers breached internet-facing Cisco Expressway gateways soon after public demonstration code appeared. The affected Expressway Core and Edge systems were clustered, allowing unauthenticated attackers with network access to run commands as root. Investigators said the attackers compromised two exposed…