2026-10-29 Daily Cyber News
When cyber incidents interrupt patient care, remediation priorities become operational decisions rather than technical housekeeping. Today’s issue opens with a UNM Health attack that diverted ambulances and canceled appointments, then tracks an actively exploited Brotli decoder weakness spread across cloud and enterprise stacks. It also examines Volt Typhoon’s fast-changing relay infrastructure, which is designed to hide access to high-value networks. Beyond the top three, we cover a major DHS personnel-data…
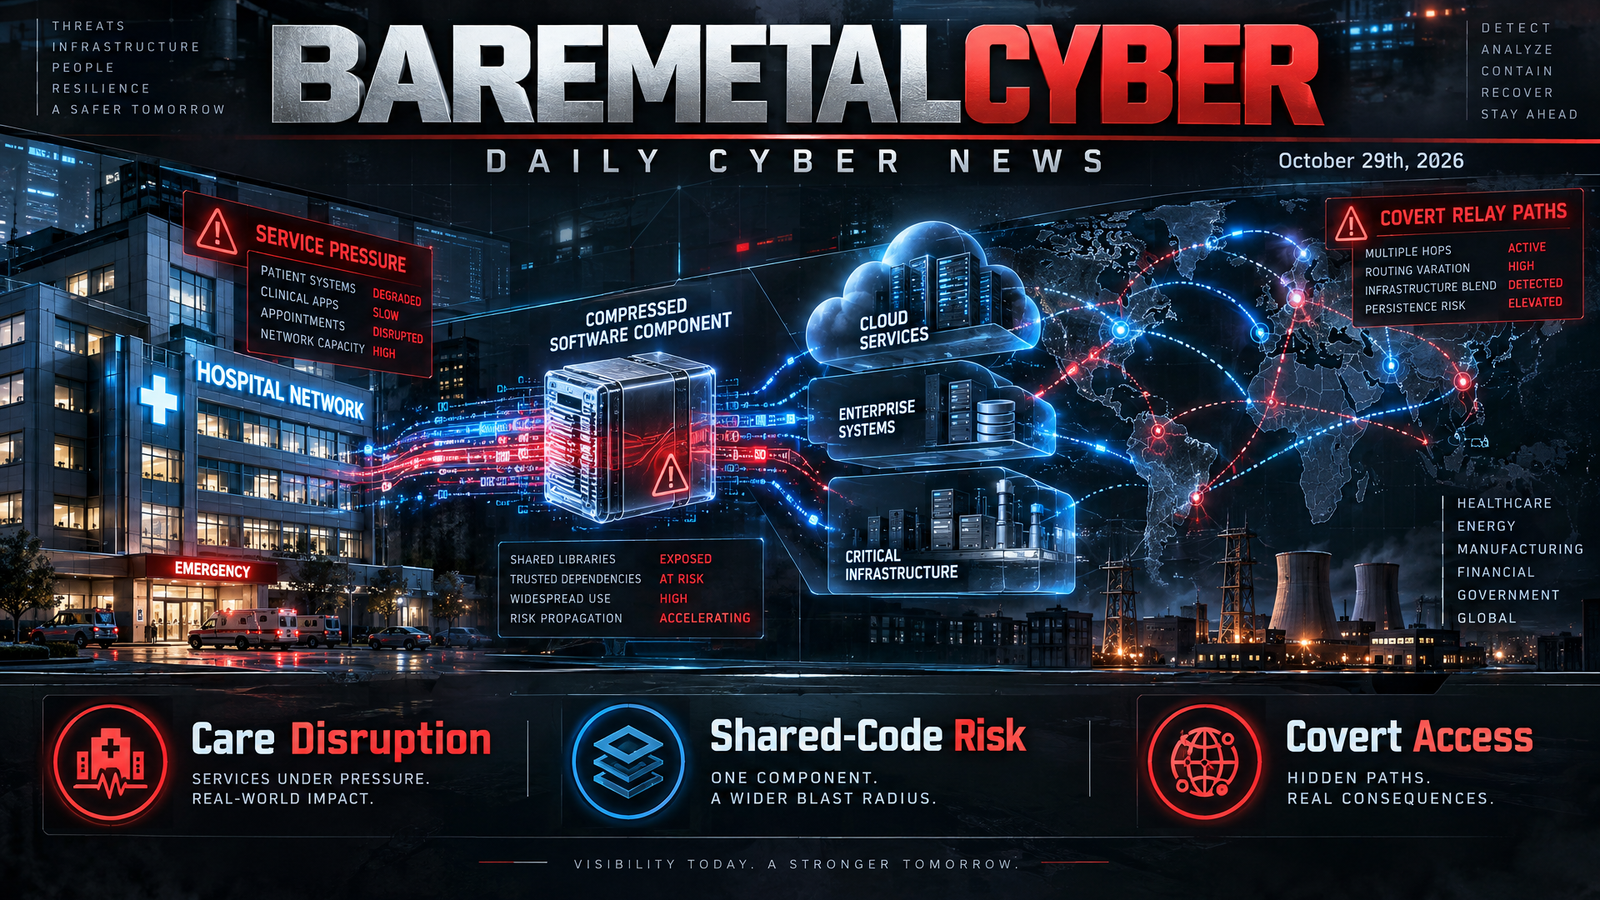
- Legal & RegulatoryCyberattack diverts ambulances and cancels care at UNM Health
Patient care was disrupted when a cyberattack knocked critical electronic systems offline across UNM Health on October 26. Ambulances were diverted for two hours, appointments and outpatient surgeries were canceled, and new patients were temporarily limited. Hospitals stayed open, and critical systems and…
- Vulnerabilities & ExploitsWidely used Brotli decoder puts cloud and enterprise apps at risk
Organizations now have to trace a critical Brotli decoder issue through cloud runtimes, developer stacks, and products that bundle the library. Crafted compressed input can cause memory corruption, expose process memory, crash services, or allow code execution without authentication. The issue is listed…
- Vulnerabilities & ExploitsVolt Typhoon rebuilds covert attack paths in under two minutes
Critical infrastructure defenders face an access network that can be rebuilt faster than traditional blocklists can keep up. Volt Typhoon has used rotating chains of compromised routers, connected devices, and enterprise systems to hide operations against high-value targets. Researchers observed chains…
- Security OperationsDHS personnel leak exposes identities and internal access clues
More than 40,000 DHS personnel records were published online, exposing names, roles, work contacts, office locations, and details tied to internal access. The dataset includes large numbers of CBP and ICE personnel, cybersecurity staff, and senior officials. A hacker claimed the records came from a DHS…
- Vulnerabilities & ExploitsFirewall attacks turn edge access into internal credential theft
Attackers turned exposed firewalls into a route toward credentials and internal administration. A reported China-linked operation scanned 19,000 internet-facing devices, narrowed the set to 240 potential targets, and exploited 25 during October 23-24, reportedly placing root webshells on 24. Activity…
- Cloud SecurityGhostAction keeps stolen developer tokens alive after blocked attacks
Blocked malicious workflows did not eliminate the accounts behind the GhostAction supply-chain campaign. Attackers pushed 72,000 commits to 23,000 public repositories between October 13 and 21, including 8,000 new targets. GitHub prevented the workflows from executing, yet researchers found persistent…
- Government & PolicyCisco SD-WAN compromise threatens control-plane trust and keys
Organizations using Cisco Catalyst SD-WAN face both a critical access path and evidence of purpose-built post-compromise tooling. A peering authentication weakness can let an unauthenticated remote attacker gain a high-privileged internal account and change fabric configuration through NETCONF. Separate…