2026-10-27 Daily Cyber News
When digital systems fail, ambulances can be diverted, clinics can close, and essential services can lose capacity within minutes. Today’s issue examines a cyberattack that disrupted New Mexico’s largest teaching hospital, urgent action around widely used PHP systems facing exploitation attempts, and a poisoned LiteLLM release traced to an exposed key that was never revoked. We also cover risks involving trading desktops, private code repositories, older Apple devices, and compromised certificate authorities.…
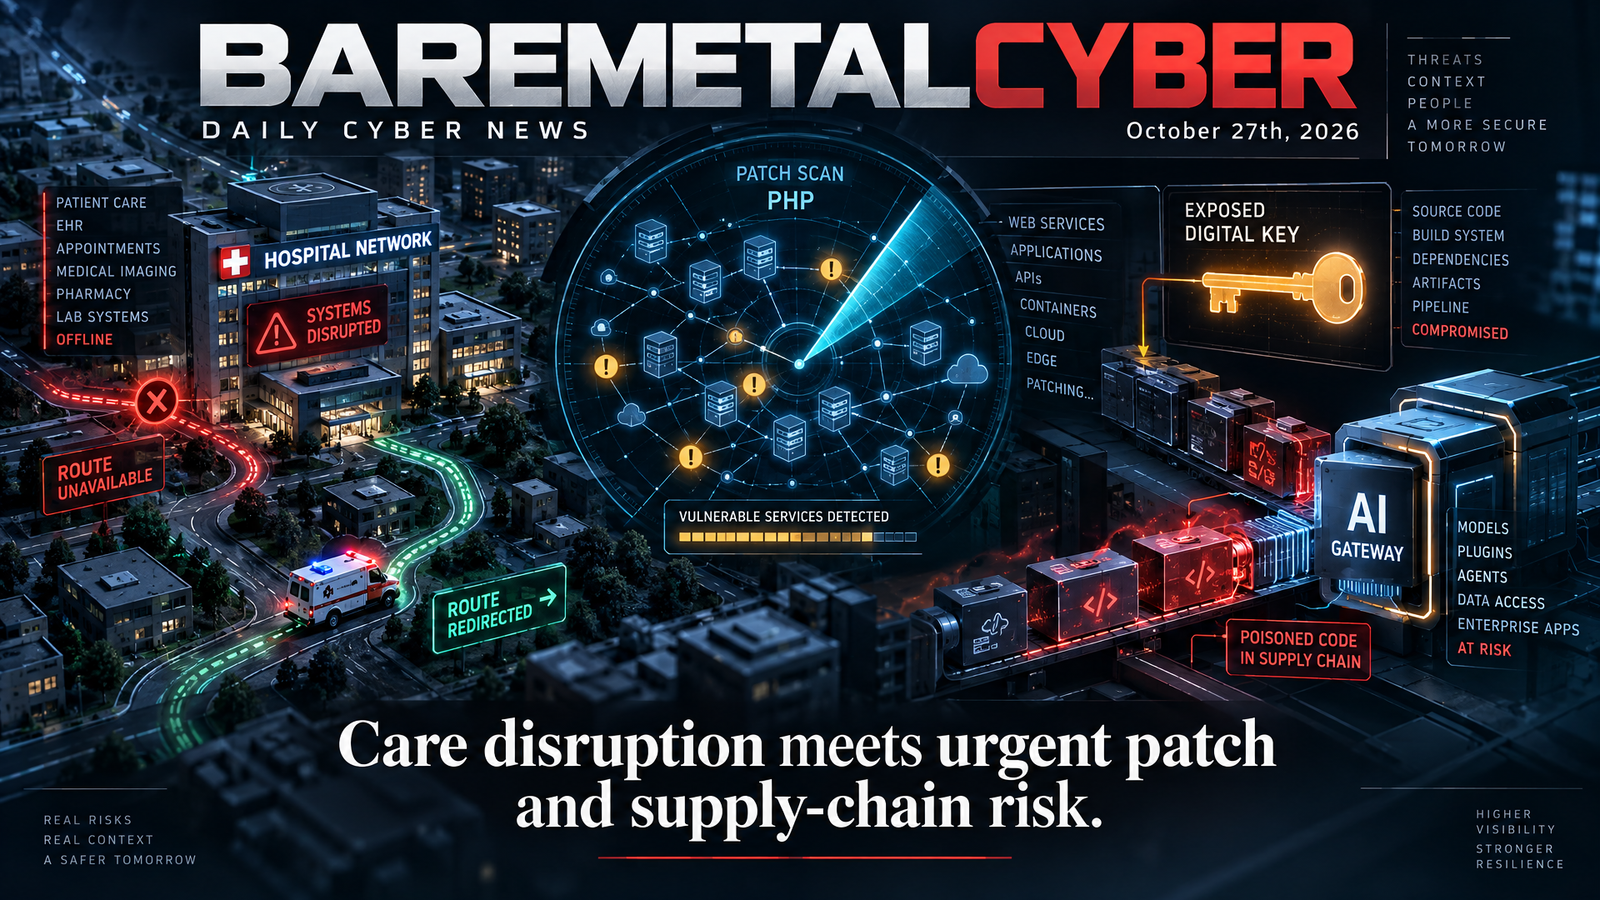
- Government & PolicyHospital cyberattack diverts ambulances and closes clinics
Patient care was disrupted when a cyberattack hit the University of New Mexico Health Sciences Center. Ambulances were diverted, appointments across more than 30 clinics were canceled, and health sciences classes were called off. Hospitals later reopened, with systems and services returning in phases. An…
- Vulnerabilities & ExploitsPHP attacks trigger an urgent inventory and patch deadline
Organizations running PHP face active exploitation attempts against two newly disclosed security issues. Federal civilian agencies were ordered to patch by Thursday, while other organizations were told to identify every PHP system and update it. Thousands of failed attack attempts have been reported…
- AI & Emerging TechnologyExposed key turns LiteLLM release into a supply-chain attack
A poisoned LiteLLM release exposed users to credential theft and remote access. The attack began with a master key accidentally published in a public repository in May and removed without being revoked. The attacker later used that key to obtain a privileged GitHub token and compromise additional…
- Identity & AccessGMO cloud breach puts trading accounts and customer data at risk
Customers of GMO Internet’s cloud desktop service face possible data theft and unauthorized trading activity. The company shut down the service after discovering unauthorized access and later said information linked to customers and its business appeared online. It warned that 26,739 virtual desktop…
- Threat IntelligenceStolen GitHub tokens drain secrets from private repositories
An active campaign is using stolen GitHub tokens to extract secrets from private repositories. More than 13,500 malicious branches were recovered across over 850 compromised accounts. The attacker plants a workflow that encodes secrets, writes them into a run log, downloads the log through GitHub’s API…
- Legal & RegulatoryApple expands targeted-attack fix to older iPhones and iPads
Older Apple devices now have protection against a security issue used in highly targeted attacks. Apple backported the fix through iOS and iPadOS 18.7.11 after initially addressing newer software in September. A maliciously crafted file could allow code execution on an affected device. Public details…
- Phishing & Social EngineeringCompromised certificate keys force Windows trust-list action
Microsoft issued an out-of-band Windows update to remove trust from certificates connected to compromised eMudhra authorities. Eight intermediate certificate private keys were found to be recoverable within seconds because of an error during key generation. Microsoft removed seven associated certificates…